A backup report can show that data was copied successfully. It cannot, by itself, show that an organization can restore a service people depend on. Cyber recovery work becomes easier to recognize when a nomination follows that difference all the way to a tested result.
The achievement might be discovering a missing dependency, making recovery instructions usable by another operator, or proving that a restored application supports an essential business task. These contributions often happen quietly, before an incident makes their value obvious.
For award reviewers, the central question is practical: what can the organization now demonstrate about recovery that it could not demonstrate before? A credible answer connects the service, the test conditions, the observed result, and the nominee's contribution.
Start with the service that needs to return
Define what recovery means for the people using the service. Restoring a database, starting a virtual machine, and completing a customer transaction are different milestones. A nomination should identify which one was actually demonstrated.
Describe the essential function, its owner, and the dependencies needed to perform it. Those might include identity services, network configuration, application settings, encryption keys, or a supplier's assistance. Explain which dependencies were included in the work and which were assumed available.
NIST's Guide for Cybersecurity Event Recovery connects resource prioritization with recovery planning and realistic test scenarios. For an award submission, that suggests starting with a service priority and a defined recovery question, rather than an inventory of backup products.
Choose a bounded claim. Demonstrating recovery of one important workflow can be a substantial achievement. Presenting that result as proof that the whole organization can recover makes the evidence less credible.
Explain why the starting condition mattered. Perhaps nobody had restored the application with its current configuration, or the only instructions depended on one administrator's memory. That context helps reviewers understand the value of the improvement.
State exactly what the test exercised
A discussion, a file restore, an application rebuild, and a service recovery test establish different things. Describe the activity in plain language before drawing conclusions from it.
Specify the environment, data set, recovery materials, participating roles, and conditions assumed at the start. If infrastructure was already prepared or credentials were supplied in advance, say so. Those choices may be appropriate for a focused test, but they affect what the result means.
A tabletop can uncover uncertainty about authority or priorities. It does not establish that a technical restore works. Our guide to recognizing cybersecurity tabletop exercises that improve readiness explains how to assess discussion-based preparation. Keep that evidence distinct from the hands-on restoration described here.
Use approved test arrangements, with isolation and safeguards appropriate to the systems and data involved. Reviewers should reward a well-controlled test with clear limits. Disrupting production to make a demonstration seem more realistic is not an achievement in itself.
Check whether recovery materials are actually available
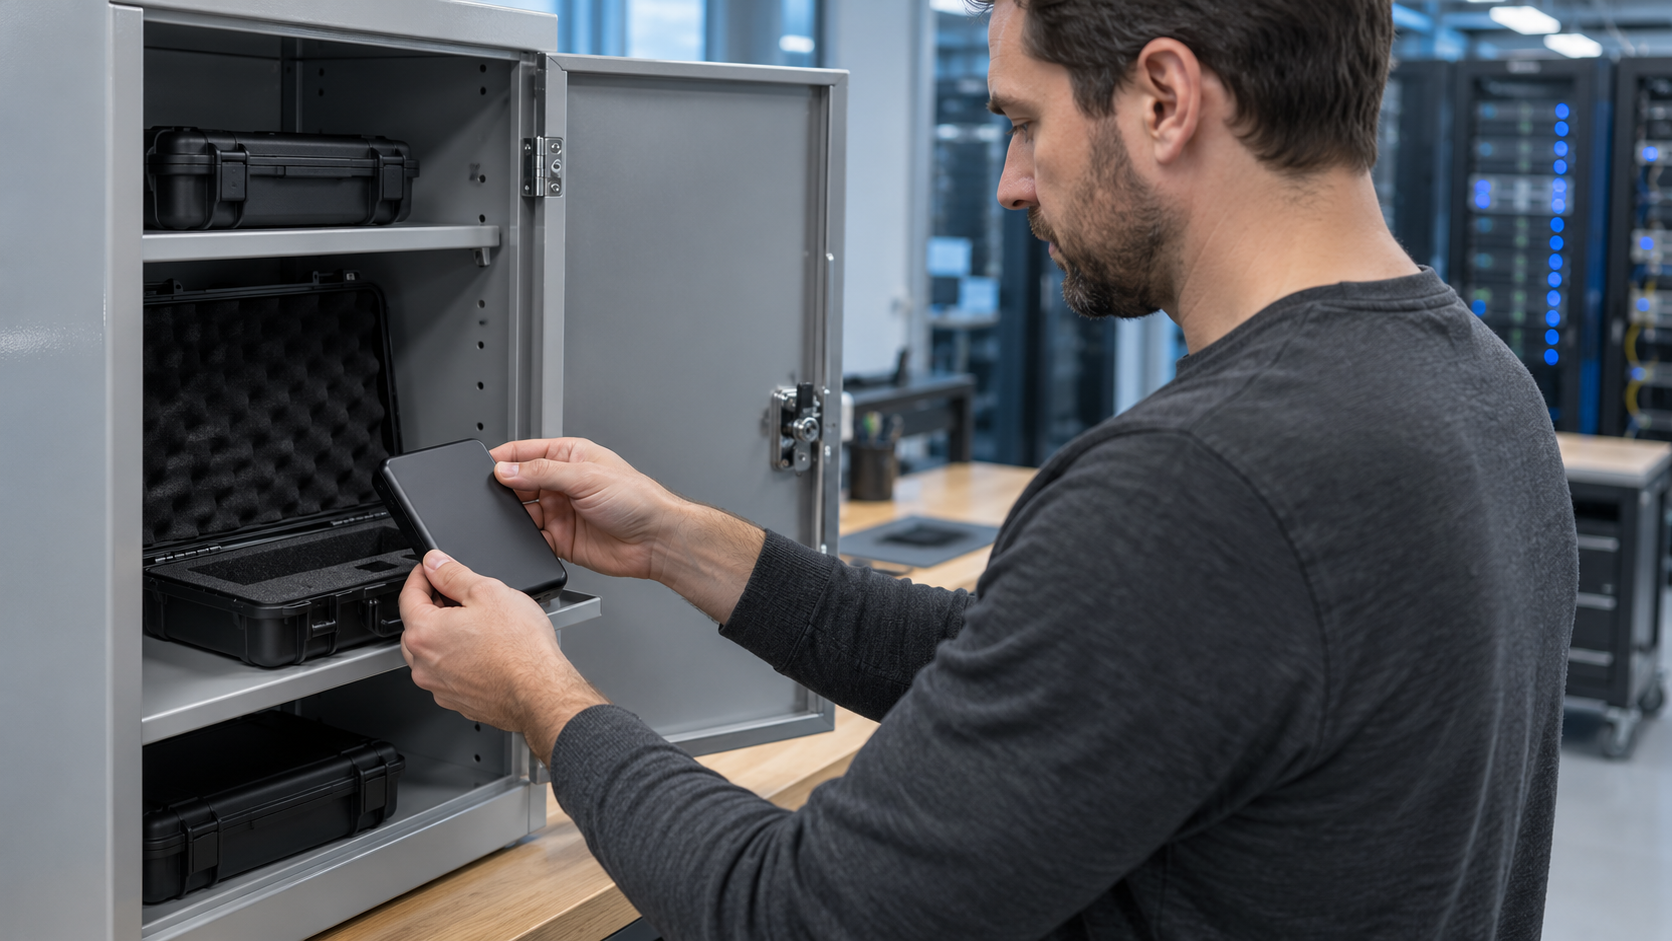
Recovery depends on more than possessing a backup. The people performing the work need authorized access to the correct recovery materials under the conditions being tested.
The joint CISA #StopRansomware Guide recommends maintaining offline, encrypted backups of critical data and regularly testing their availability and integrity in a disaster recovery scenario. For recognition, the useful evidence is what the team checked and what that check revealed.
Could an authorized operator obtain the backup, instructions, required software, and relevant keys? Did the process depend on an account or system that the scenario treated as unavailable? Was a provider expected to perform a step that had never been agreed?
Do not include secrets or sensitive storage details in a nomination. An approved summary can describe the access condition, the responsible role, the observed obstacle, and the change made.
Credit the person who exposed a circular dependency or corrected an unusable access procedure. Purchasing protected storage may support the work, but a procurement record alone does not demonstrate recoverability.
Verify that the restored service is usable
A successful restore job is an intermediate result. Reviewers need to understand how the team checked the recovered service and who accepted the outcome.
Describe appropriate technical and business checks. These might include confirming that expected records are present, checking application behavior, verifying access permissions, and completing an agreed workflow. State what passed, what failed, and what remained outside the test.
In a hypothetical example, a team restores an order-processing application in an isolated environment. The database opens, but a service owner discovers that an attachment store was excluded. The team updates the recovery procedure, restores that dependency, and repeats the agreed workflow successfully. The contribution is the verified improvement, not the initial green backup status.
Cyber recovery also requires attention to trust in the recovered environment. Explain the checks used to assess recovery materials and the conditions for returning systems to use. CISA's recovery guidance cautions against reinfecting clean systems during restoration.
Keep the claim proportionate. A successful functional test does not prove the absence of every compromise, and restoring data does not reverse a confidentiality breach.
Separate recovery objectives from observed results
An objective describes what the organization needs. A test result describes what happened under particular conditions. Keep both visible.
A recovery time objective concerns how long recovery can take before the disruption harms the organization's mission or business processes. A recovery point objective identifies the point in time to which data must be recovered. They address different questions: service interruption and the required recoverable data state.
State the agreed objective, the observed result, and the measurement boundary. Did timing begin with incident declaration, authorization to recover, or the start of a restore job? Did it end when infrastructure started or when the service owner completed acceptance checks?
Explain how the recovered data point was verified. A backup schedule is not evidence that the expected data was successfully restored.
For before-and-after comparisons, identify changes in data volume, equipment, preparation, and scope. Faster execution may reflect a genuine improvement, a narrower test, or both. The guide to documenting cybersecurity impact for an award nomination helps turn those distinctions into an honest account of progress.
Follow failed checks through correction and retesting
A failed test can produce valuable work. Recognition should depend on what the team learned, corrected, and demonstrated afterward.
Connect each important finding to an owner and a specific action. A missing configuration file requires a different response from unclear approval authority or unavailable supplier support. Describe the correction at that level of detail.
Then show the follow-up evidence. Updating a runbook establishes that instructions changed. Repeating the relevant recovery step establishes more about whether the correction addressed the original problem.
Keep unresolved findings in view. If a dependency remains untested or an action falls outside the eligible period, state that limit. A transparent account gives reviewers firmer ground than an unexplained declaration that recovery is now assured.
Distinguish recovery demonstrated during an incident from recovery demonstrated in a planned test. Both can deserve recognition, but their constraints and evidence differ.
Credit the work that makes recovery repeatable
Recovery readiness often crosses job boundaries. An administrator may fix restoration sequencing, an application owner may define meaningful acceptance checks, and a coordinator may secure supplier participation. Attribute those contributions precisely.
For an individual nomination, explain what that person decided, built, clarified, or verified within the shared result. For a team nomination, show how the roles worked together. The perspective in the hidden heroes of cybersecurity is especially relevant to the people whose preparation prevents a future scramble.
Look for evidence that the capability can survive a handover. Could another authorized operator follow the current instructions? Are changes to applications reflected in recovery materials? Does someone own the next review or test?
Do not require a small team to imitate a large organization's tooling. Judge the quality of its evidence, the difficulty of the starting problem, and the usefulness of the demonstrated result in context.
Build the submission around one demonstrated improvement
Before submitting, check that the nomination answers these questions:
- What needed to recover? Name the service, essential workflow, and starting uncertainty.
- What was tested? Describe the scope, environment, assumptions, and safeguards.
- What proved the result? Identify technical checks, service-owner acceptance, and measurement boundaries.
- What changed after problems appeared? Connect findings to corrections and relevant retests.
- Who made the difference? Attribute contributions and show what others can now repeat.
Use authorized evidence summaries and approved extracts, removing credentials, personal data, and sensitive system details. Follow the award program's permitted process when fuller verification must remain confidential.
Cyber recovery recognition should make dependable preparation visible. A clear nomination shows a service restored under stated conditions, a result checked by the right people, and a contribution that leaves the organization better prepared for the next disruption.